Data Recovery Heroes.
Recovery Italia® può aiutarVi a risolvere con successo qualsiasi caso di perdita di dati.
preventivo immediatoRecovery Italia® può aiutarVi a risolvere con successo qualsiasi caso di perdita di dati.
preventivo immediatoUn nuovo attacco ransomware il "BEAST" afferma di essere veloce stabile ed invulnerabile.
E' davvero così ? In questo caso affrontiamo il caso di una azienda informatica brasiliana colpita direttamente con una escalation sui server ESX Vmware.
Non risultavano essere presenti backup Veeam o backup alternativi.
You have been attacked by BEAST the fastest, most stable, and most invulnerable ransomware
YOUR PERSONAL ID: XXXXXX-XXXX-XXXX-XXXX-XXXXXXXX
Unfortunately for you, a major IT security weakness left you open to attack, your files have been encrypted
The only method of recovering files is to purchase decrypt tool and unique key for you.
If you want to recover your files, write us to this e-mail: start.of.transaction@onionmail.org
In case of no answer in 24 hours write us to this backup e-mail: start.of.transaction@mailum.com
Check your e-mail "Spam" or "Junk" folder if you don't get answer more than 6 hours.
Sometimes you will have to wait some time for our reply, this is because we have a lot of work and we attack hundreds of companies around the world.
Contact us soon, because those who don't have their data leaked in our press release blog and the price they'll have to pay will go up significantly.
Attention!
Do not rename encrypted files.
Do not try to decrypt your data using third party software - it may cause permanent data loss.
We are always ready to cooperate and find the best way to solve your problem.
The faster you write - the more favorable conditions will be for you.
Our company values its reputation. We give all guarantees of your files decryption.
What is the guarantee that we won't scam you?
We are the oldest extortion gang on the planet and nothing is more important to us than our reputation. We are not a politically motivated group and want nothing but financial rewards for our work. If we defraud even one client, other clients will not pay us. In 7 years, not a single client has been left dissatisfied after making a deal with us. If you pay the ransom, we will fulfill all the terms we agreed upon during the negotiation process. Treat this situation simply as a paid training session for your system administrators, because it was the misconfiguration of your corporate network that allowed us to attack you. Our pentesting services should be paid for the same way you pay your system administrators' salaries.
What are your recommendations?
- Never change the name of the files, if you want to manipulate the files, be sure to back them up. If there are any problems with the files, we are not responsible for them.
- Never work with intermediary companies because they charge you more money.Don't be afraid of us, just email us.
- Not a single company that paid us has had issues. Any excuses are just for insurance company to not pay on their obligation.
Sensitive data on your system was DOWNLOADED.
If you DON'T WANT your sensitive data to be PUBLISHED you have to act quickly.
Data includes:
- Employees personal data, CVs, DL, SSN.
- Complete network map including credentials for local and remote services.
- Private financial information including: clients data, bills, budgets, annual reports, bank statements.
- Manufacturing documents including: datagrams, schemas, drawings in solidworks format
- And more...
What are the dangers of leaking your company's data.
First of all, you will receive fines from the government such as the GDRP and many others, you can be sued by customers of your firm for leaking information that was confidential. Your leaked data will be used by all the hackers on the planet for various unpleasant things. For example, social engineering, your employees' personal data can be used to re-infiltrate your company. Bank details and passports can be used to create bank accounts and online wallets through which criminal money will be laundered. On another vacation trip, you will have to explain to the FBI where you got millions of dollars worth of stolen cryptocurrency transferred through your accounts on cryptocurrency exchanges. Your personal information could be used to make loans or buy appliances. You would later have to prove in court that it wasn't you who took out the loan and pay off someone else's loan. Your competitors may use the stolen information to steal technology or to improve their processes, your working methods, suppliers, investors, sponsors, employees, it will all be in the public domain. You won't be happy if your competitors lure your employees to other firms offering better wages, will you? Your competitors will use your information against you. For example, look for tax violations in the financial documents or any other violations, so you have to close your firm. According to statistics, two thirds of small and medium-sized companies close within half a year after a data breach. You will have to find and fix the vulnerabilities in your network, work with the customers affected by data leaks. All of these are very costly procedures that can exceed the cost of a ransomware buyout by a factor of hundreds. It's much easier, cheaper and faster to pay us the ransom. Well and most importantly, you will suffer a reputational loss, you have been building your company for many years, and now your reputation will be destroyed.
Do not go to the police or FBI for help and do not tell anyone that we attacked you.
They won't help and will only make your situation worse. In 7 years not a single member of our group has been caught by the police, we are top-notch hackers and never leave a trace of crime. The police will try to stop you from paying the ransom in any way they can. The first thing they will tell you is that there is no guarantee to decrypt your files and delete the stolen files, this is not true, we can do a test decryption before payment and your data will be guaranteed to be deleted because it is a matter of our reputation, we make hundreds of millions of dollars and we are not going to lose income because of your files. It is very beneficial for the police and the FBI to let everyone on the planet know about the leak of your data, because then your state will receive fines under GDPR and other similar laws. The fines will go to fund the police and FBI. The police and FBI will not be able to stop lawsuits from your customers for leaking personal and private information. The police and FBI will not protect you from repeat attacks. Paying us a ransom is much cheaper and more profitable than paying fines and legal fees.
If you do not pay the ransom, we will attack your company again in the future.
L'attacco è stato eseguito con una progressione di encryption variabile, orientata al danneggiamento specifico dei file vmdk.
L'encryption si è concentrata nella prima zona del virtual disk danneggiandola in modo significativo, e si è focalizzata anche sulla coda del file, con lo scopo di danneggiare i backup delle partizioni GPT.
Per poter garantire una encryption di tipo orizzontale rapida, l'attacco non si è propagato su tutto il virtual disk e questo ha consentito una analisi dei contenuti a prescindere dalle strutture di base compromesse.
Nello specifico l'azienda colpita Utilizzava Database di Firebird, dei quali esistevano molti backup interni.
Sebbene i metadati di base del file system NTFS fossero stati compromessi da un long stripe di attacco, superiore ai 3M di settori logici, il file system risultava essere in buono stato su tutte le Virtual Machine Colpite.
Il risultato di recovery è stato ottenuto eseguendo un blending delle pagine dei Database Firebird danneggiate dagli stripe di encryption con le posizioni di backup dello stesso Firebird.
La regola più importante da seguire in caso di attacco hacker su ESX è di lasciare inalterato lo scenario del datastore e scollegarlo dalla rete aziendale.
E' possibile eseguire aquisizione forense sia degli storage interni che del sistema operativo utilizzando una connessione SSH in una virtual lan isolata.
Se abbiamo urgenza di scaricare le VM per il Data Recovery è consigliabile usare la procedura di Download via HTTP direttamente da VMWARE Sphere dall'interfaccia Web di management.
Una successiva analisi offline delle macchine virtuali sarà necessaria per valutare la tipologia di attacco e la densità degli stripe generati dall'encryptor.
E' importante non eseguire alcuna scrittura sul server esx ( come la creazione o la copia di vm ) in quanto nel file system vmfs potrebbero trovarsi elementi utili per recuperare le vm colpite, come snapshot cancellati o vm cancellate durante l'attacco.
In tutti i casi di attacco su scala enterprise incontrati negli ultimi 5 anni, che hanno coinvolto datastore, Veeam backup o HYPER-V abbiamo sempre ottenuto successo nel recovery e nel ripristino dei dati.
Agire di impulso e cedere al ricatto non garantirà in alcun modo che i dati esfiltrati non vengano distribuiti/venduti nel cyberspazio.
Aziende competenti e preparate per intervenire con tempestività ed efficacia esistono e possono risolvere il problema, spesso ad una frazione del costo del Ransomware.
Contatta il nostro call center o inviaci una richiesta di assistenza a info@recoveryitalia.it. I nostri esperti sono a tua completa disposizione per una consulenza gratuita.
Subito un attacco? Scopri come gestire il recupero dati dopo un attacco ransomware. Guida su cosa fare, cosa evitare e come non perdere i file criptati.
I File Veeam sono strategici per la vita di una azienda e rappresentano la posizione di restore per il recovery delle infrastrutture in seguito a crash del datacenter.Tuttavia è possibile che possano non funzionare a causa di corruzione disco o attacco Ransomware.
Formattare per errore una card è un errore comune e recuperare i dati utilizzando programmi per il recupero è molto semplice. Ma cosa accade se i file che dobbiamo salvare risultano essere frammentati ?
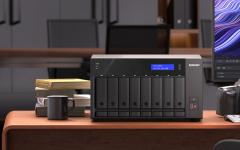
La sostituzione di un disco danneggiato in un NAS QNAP comporta la ricostruzione ( rebuild ) del RAID. In molti casi la procedura puo interrompersi o non rendere disponibile il volume e i dati.
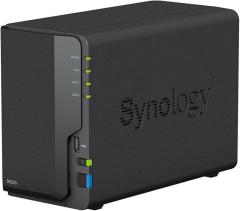
In questo caso affrontiamo un nuovo tipo di attacco specifico per NAS Synology dove gli attaccanti hanno avuto accesso privilegiato al sistema e occultato il volume dati
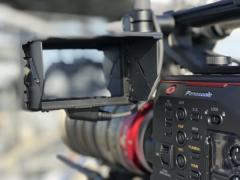
Durante uno shooting è possibile che card possano essere invertite ed utilizzate o formattare per errore. E' possibile recuperarare un girato parzialmente sovrascritto in una sd card ?
Sedi Operative
Procedura recupero dati
Richiesta Pickup
Richiesta Assistenza
Listino Prezzi
Preventivo ON LINE
Contatto
Privacy Policy
Recupero dati da Qualsiasi Device
Hard Disk Drive
Hard Disk USB
Pen Drive USB
Enterprise Servers
Sistemi RAID
NAS & DAS
Cellulari e Smartphone
Mobile Data Rescue
WhatsApp Data Recovery
iPhone Data Recovery
Challenger Rocket
Challenger PCI Board
DATA RECOVERY SERVICE SRL
Via del Fosso Centroni, 4 Roma (RM)
PIVA.: 14931361001
Via del fosso centroni, 4
00118 ROMA
Call Center 39 06 98357672
Email: info@recoveryitalia.it
 METRO A ANAGNINA
Via Attilio Regolo 19
00192 ROMA
Call Center 39 06 98357672
Email: info@recoveryitalia.it
METRO A LEPANTO
Via Dante, 16
21221 Milano
Call Center 39 02 00611518
Email: info@recoveryitalia.it
METRO M3 MISSORI